
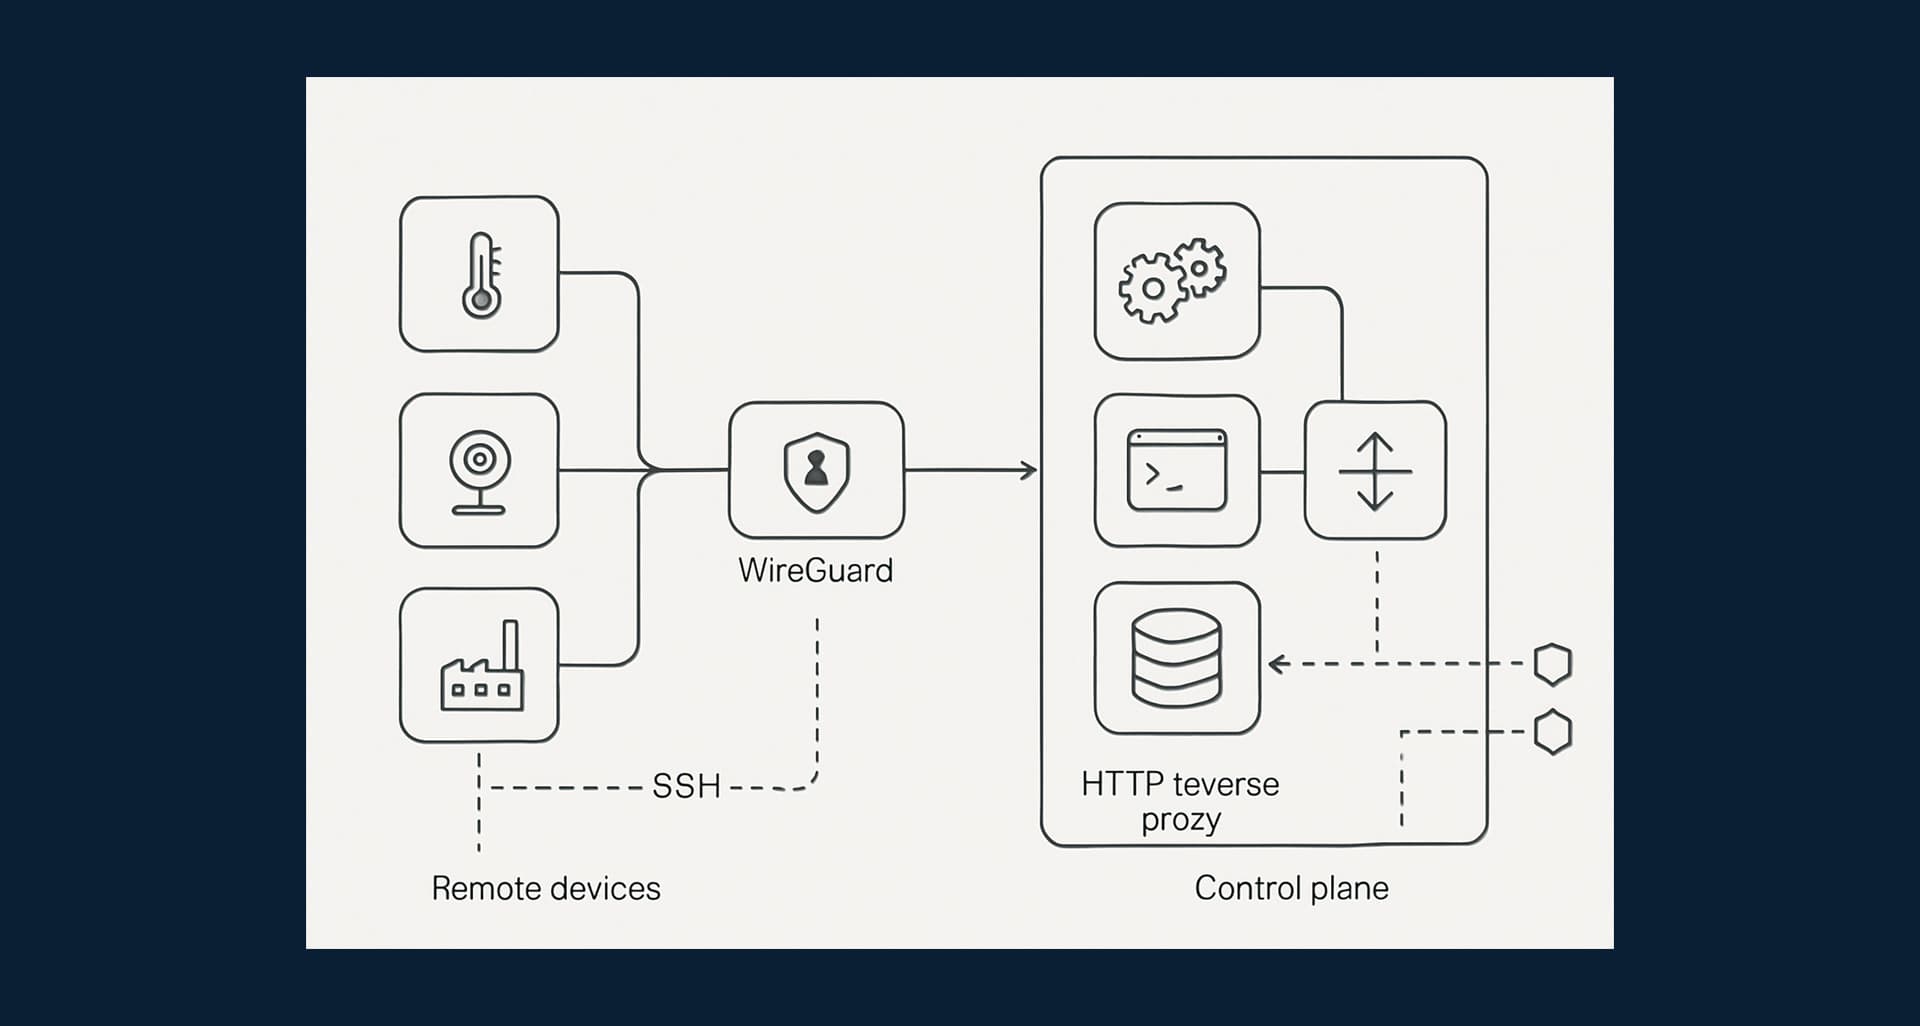
MeteorCloud is being designed around a simple split between private infrastructure access and public application delivery. For device connectivity, the plan is to use WireGuard as the private network layer. That creates a direct path to devices for internal communication and SSH access without putting those devices on the public internet. For user-facing applications, the plan is to place an HTTP reverse proxy in front of deployed services. That makes it possible to serve applications through friendly HTTPS URLs such as boiler.dashboard.meteor-edge.com instead of exposing raw ports or requiring users to track internal addresses. A key part of the approach is automatic endpoint registration. When a new application is deployed, the routing layer should learn about it without requiring manual proxy edits for each service. The architecture is also intended to stay modular and self-hosted, so networking, proxying, and application services can be operated as separate concerns.